Compliance that keeps running.
Every control owned, every deadline counted down, every audit ready. 15 frameworks, from ISO 27001, GDPR and NIS2 to CyFun and the Cyber Resilience Act, in one EU-hosted workspace.
Free for one user. No card needed.
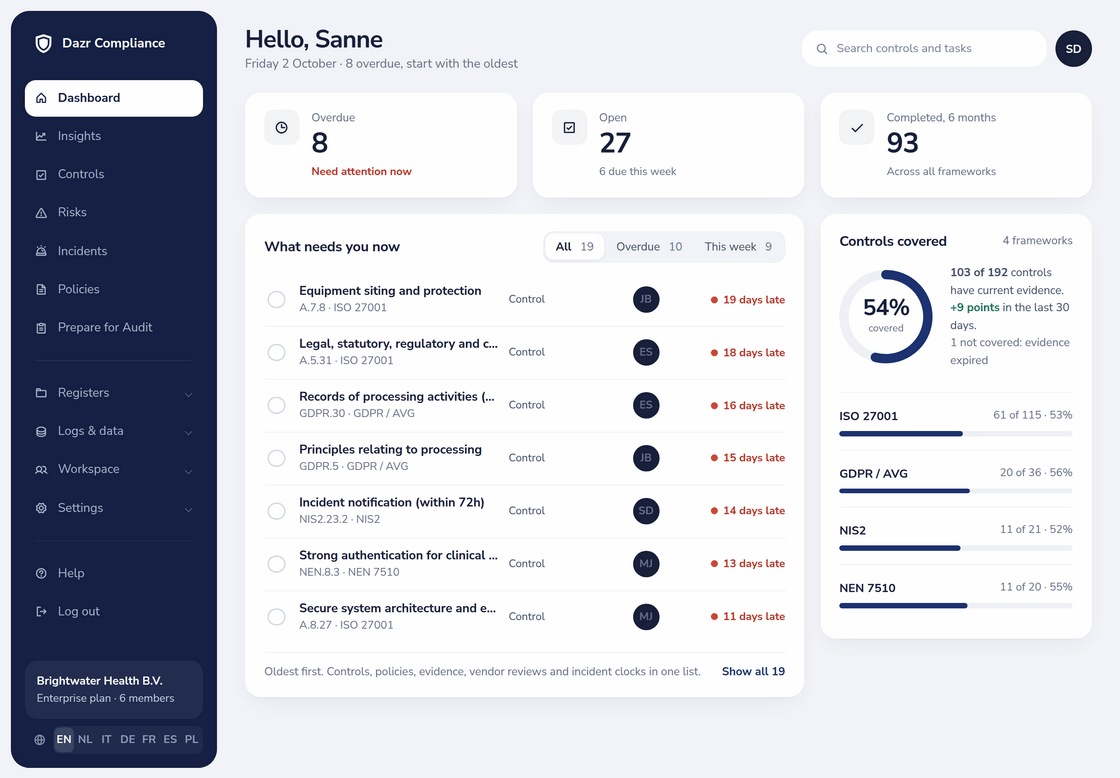
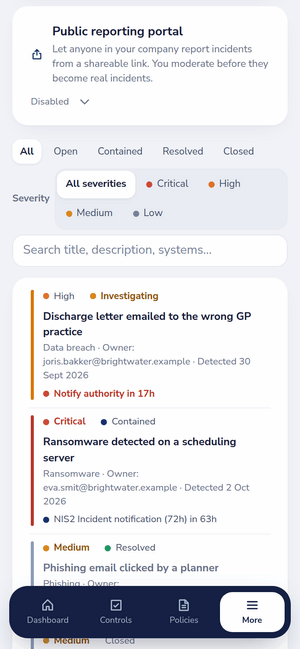
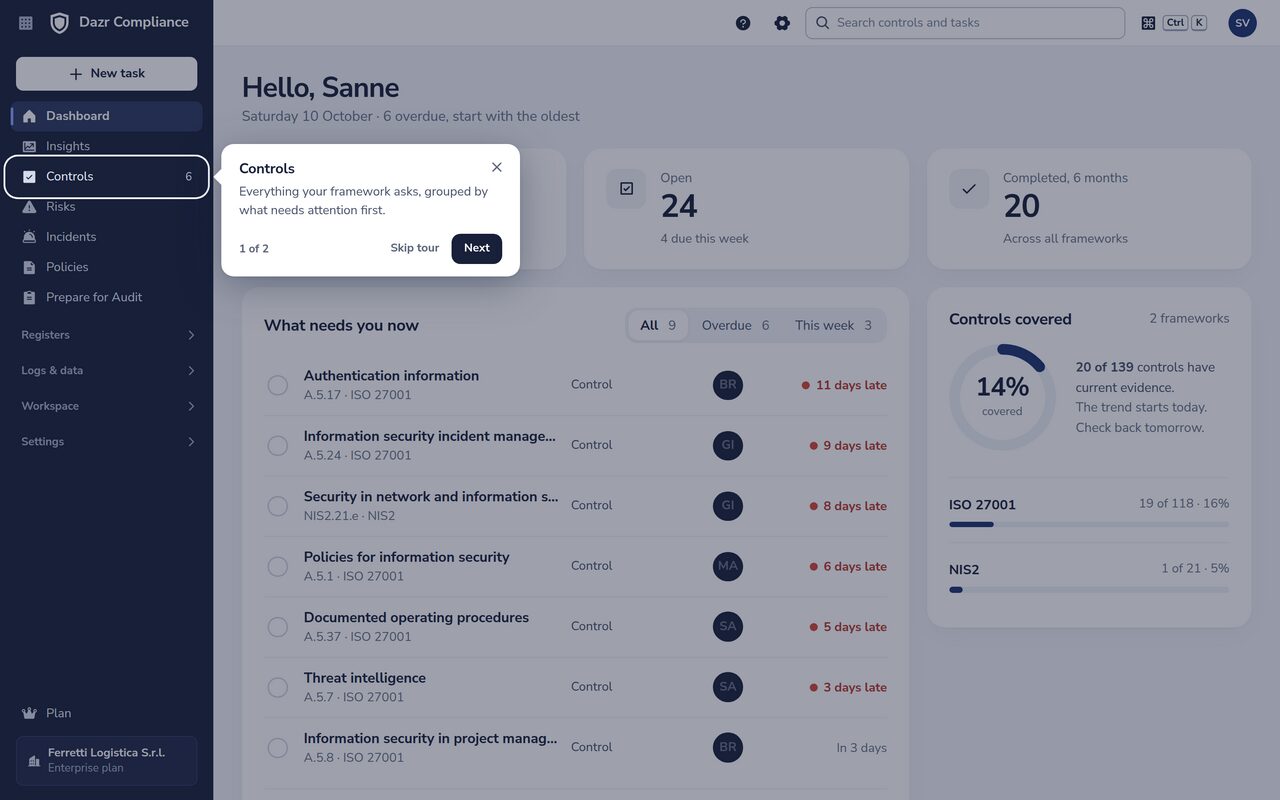
The dashboard: overdue work, this week, and coverage per framework. On the right, the incident register on a phone.
Add frameworks without rebuilding. ISO 27001:2022 includes all 93 Annex A controls and clauses 4-10. For NIS2 in Italy and Czechia, ACN’s baseline measures and NÚKIB’s measures under Decrees 409/2025 and 410/2025 are ready-made frameworks too.
Pick a module, see the screen.
Real screens from a demo workspace. Click a tab to switch.
Every control, owned and on schedule.
Each control comes with a description, a recommendation and a review cadence. Assign an owner, attach evidence and set how long it stays valid, then link it to the risks, policies and processes it covers. Reminders, weekly overdue chasers and a daily expiry digest keep it moving, with or without a consultant.
ISMS and controls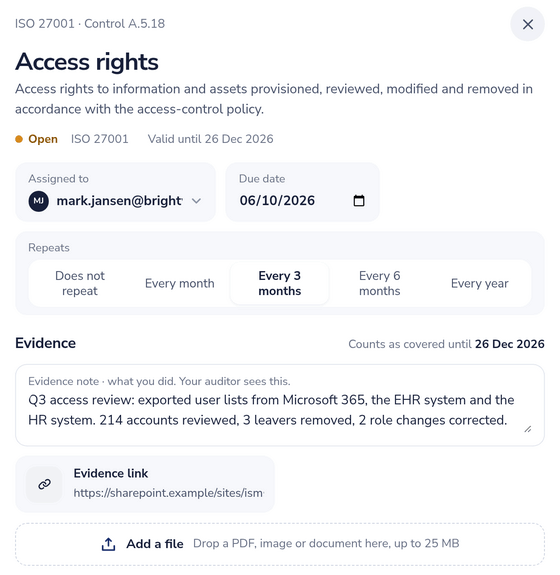
See risk before and after controls.
Score likelihood and impact on 5-point scales, inherent and residual side by side. Pick a treatment, an owner and a deadline. Accepting a risk records the rationale and a server-stamped approver.
Risk management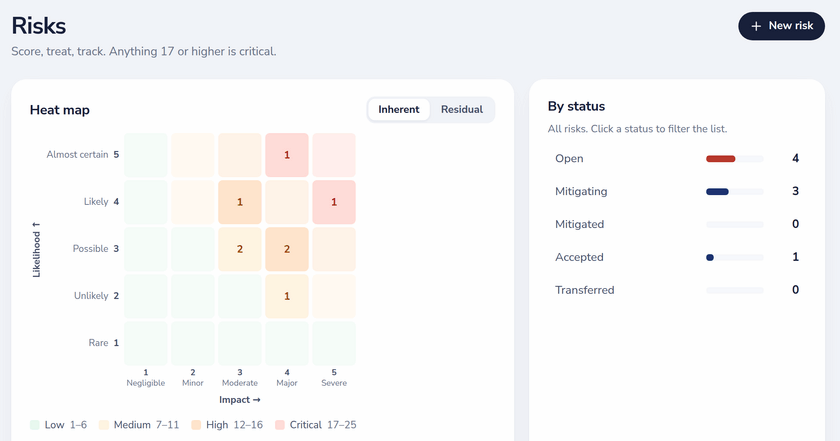
Every deadline, counted down.
Log an incident and the clocks start: 72 hours for GDPR Art. 33; 24 hours, 72 hours and one month for NIS2. A checker based on Regulation (EU) 2024/2690 flags significant incidents. On Enterprise, a public reporting page feeds your queue.
Incident management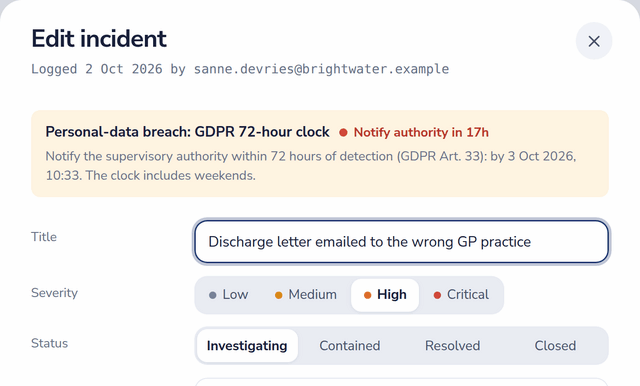
Give your auditor a login.
Invite an auditor for 1 to 60 days. They sign in with a one-time code and read every register, with room to comment. Export the approved Statement of Applicability and a PDF audit trail; on Enterprise, Prepare for Audit scores your readiness.
Audit management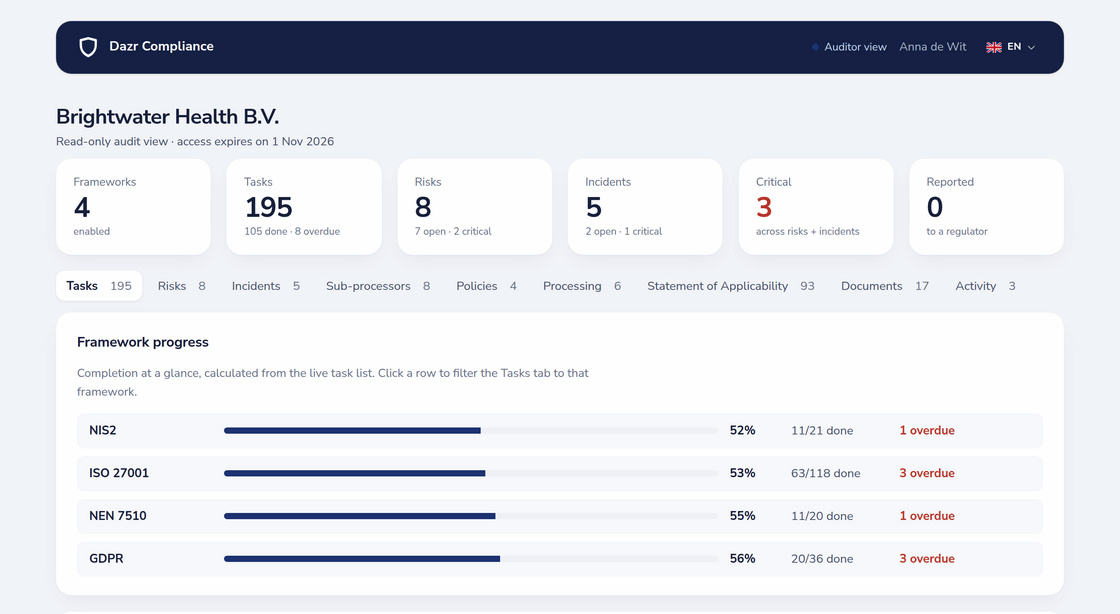
Privacy records that stay current.
Keep the Art. 30 record of processing and your DPIAs linked to the vendors and risks behind them. Every vendor carries its DPA, certificates, data access and a review date that reminds you.
Privacy (RoPA and DPIA)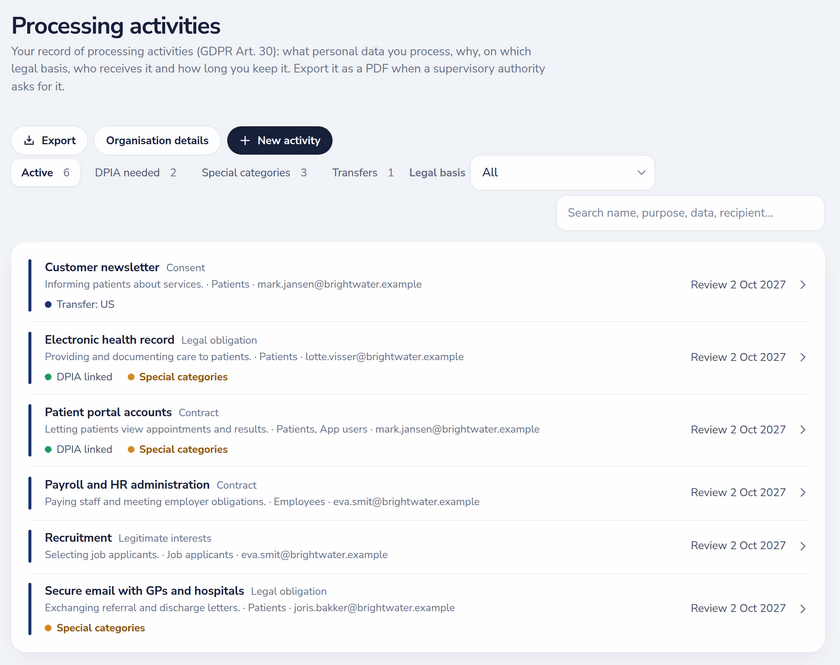
Policies people actually read.
Start from a template, approve, publish and see per version who acknowledged it. Answer customer security questionnaires once on a trust page and share one link; sensitive answers wait for your approval.
Policy management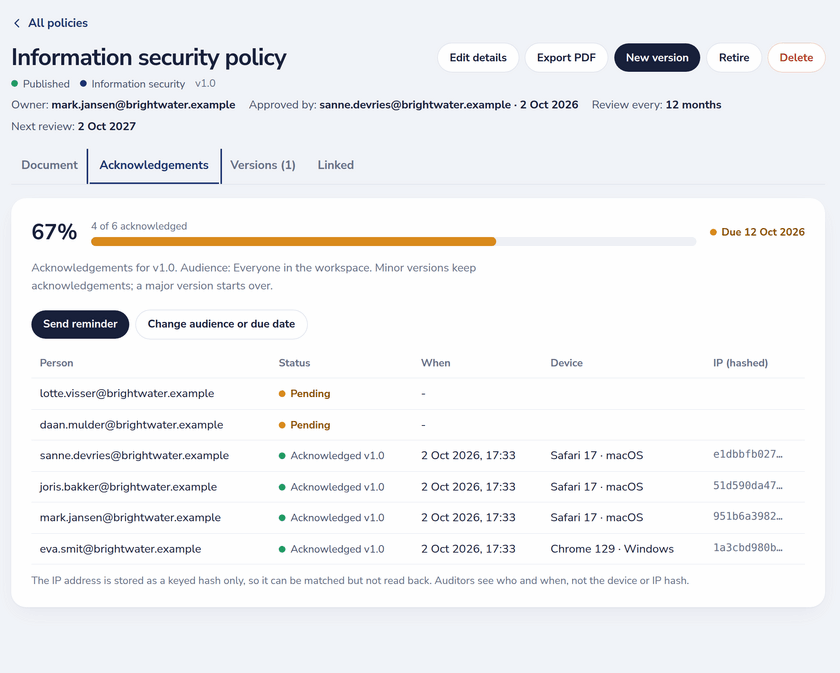
One platform, nine modules.
Each with its own page and factsheet.
Built for enterprise scrutiny.
What security and procurement will ask, answered.
- Vendor
- Dazr, Italy (VAT IT 02801250065)
- Built for
- Care providers, public bodies, financial entities, SaaS suppliers, managed service providers, and device makers and manufacturers under the Cyber Resilience Act
- Getting started
- Self-serve sign-in; guided implementation on Enterprise
Learn it on the real screen.
Own your first control, write your first policy or practise an incident: open Help, the ? at the top, and a guided tour shows you each step on the real screen, in your language.
For everything else, the help centre has a step-by-step article with real screenshots.
Public pricing.
Per month, excl. VAT. Billed monthly, cancel any time.
Several entities, custom integrations or a dedicated success manager? Custom is priced on request. Compare every feature
Who is behind Dazr.
An independent European software company.
Dazr is a software company registered in Italy. It is independent and self-funded, and Dazr Suite is its main product. Prices, plans, the sub-processors and the security measures are public, so you can check what you buy before you talk to anyone.
- Company
- Dazr, Arquata Scrivia, Italy
- Funding
- Independent and self-funded
See it with your frameworks.
Sign in with Google, Microsoft or your work email, no card. Or book a demo with our team.
Free tools and guides: a breach deadline calculator, NIS2 significant-incident and scope checks, an ISO 27001 audit estimator, guides on NIS2, DORA, the AI Act and the CRA, and country pages for the Netherlands, Italy, Poland and Belgium (Nederlands, français).