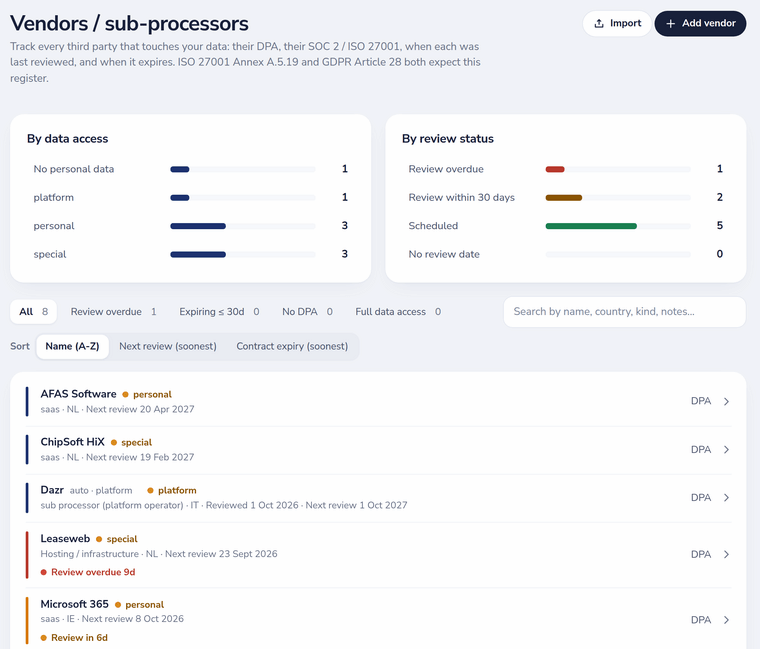
The vendor and sub-processor register
ISO 27001 Annex A.5.19 and GDPR Article 28 both expect a register of the third parties you rely on. Each vendor records its kind (SaaS, hosting, payment and more), country, the data it can access (none, personal or special-category), a link to its DPA and its certificates such as ISO 27001 or SOC 2, notes, a next review date and a contract-expiry date.
- Two charts show vendors by data access and by review status: overdue, due within 30 days, scheduled or without a date.
- Filter on review overdue, contract expiring within 30 days, no DPA or full data access; sort by name, next review or contract expiry.
- Vendor reviews that are due arrive in the same daily digest as expiring evidence.
The asset inventory
One inventory for hardware, applications, databases and other assets, each with an owner, a criticality and a classification. Assets link to processing activities, risks, processes and controls, so you can see what depends on what.
Import, export and the trust page
- Download the vendor and asset registers as Excel and CSV from Basic upwards.
- On Enterprise, import existing registers from Excel or CSV with column mapping and a preview.
- Choose which vendors appear as sub-processors on your public trust page.
- Auditors read both registers in their own portal; vendor events go out as webhooks on Enterprise.