Home › Frameworks › ISO 27001

ISO 27001 compliance software.

All 93 Annex A controls and clauses 4 to 10 run on schedule, with owners, evidence and reminders. When the auditor arrives, your Statement of Applicability, risk register and activity log are ready. Free for one framework; paid plans from €99 a month.

At a glance

  • A.5 Organisational: 37 controls covering policies, roles, supplier relationships, threat intelligence, incident response.
  • A.6 People: 8 controls on screening, terms of employment, awareness, disciplinary process.
  • A.7 Physical: 14 controls on perimeter, equipment, secure disposal, clear desk.
  • A.8 Technological: 34 controls on access control, cryptography, logging, vulnerability management, BCP-IT.

On this page

  1. What is ISO 27001?
  2. Who needs to comply
  3. Key ISO 27001 controls covered by Dazr
  4. What auditors look for
  5. How Dazr helps with ISO 27001

What is ISO 27001?

ISO/IEC 27001:2022. B2B SaaS companies, consultancies, financial services, healthcare and any organisation whose customers ask for an ISO 27001 certificate during procurement.

Who needs to comply

  • B2B SaaS companies whose customers require ISO 27001 in procurement
  • Managed-service providers (MSPs) and consultancies
  • Financial services and fintech preparing for DORA on top of ISO 27001
  • Healthcare organisations layering NEN 7510 onto ISO 27001

Key ISO 27001 controls covered by Dazr

A.5 Organisational37 controls covering policies, roles, supplier relationships, threat intelligence, incident response.
A.6 People8 controls on screening, terms of employment, awareness, disciplinary process.
A.7 Physical14 controls on perimeter, equipment, secure disposal, clear desk.
A.8 Technological34 controls on access control, cryptography, logging, vulnerability management, BCP-IT.

What auditors look for

A stage-1 audit is documentation review; stage-2 is evidence sampling. Dazr is built around stage-2: every control recurs with an owner, evidence, and an activity log entry on completion.

How Dazr helps with ISO 27001

With Dazr Compliance you can:

  • Maintain the Statement of Applicability in the portal: applicability and justification per control, approved versions, PDF and XLSX export
  • Run quarterly access reviews, annual management reviews and risk-treatment reviews on cadence with email reminders
  • Hold the risk register with inherent and residual heatmaps, treatment options and recorded risk acceptance (from Pro)
  • Operate the incident register with regulator-notification fields
  • Hand the auditor a read-only view for stage-2 sampling, or hand them a single-PDF audit trail
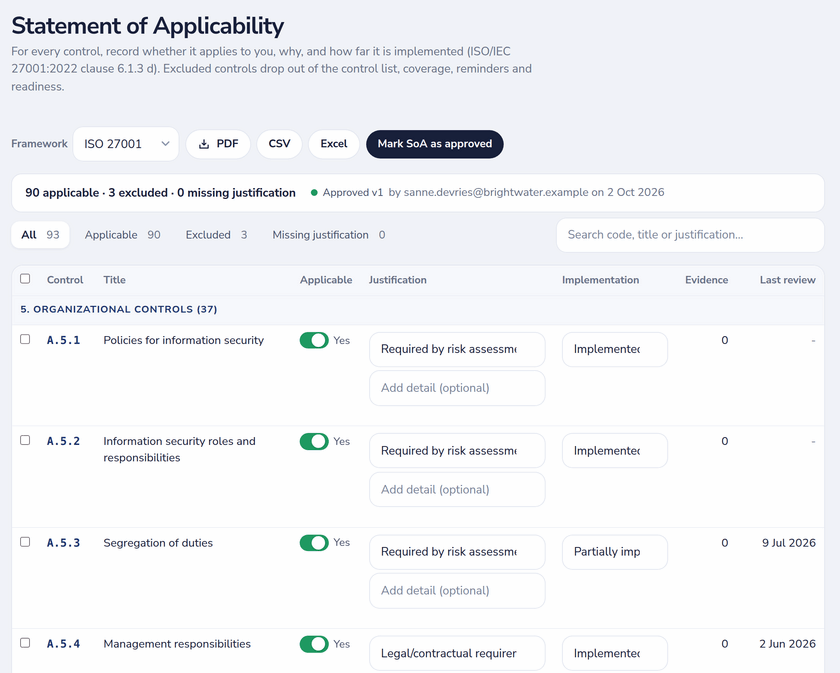
ISO 27001 Statement of Applicability with applicability, justification, implementation status and an approved version
The Statement of Applicability: applicability, justification and implementation per control, with the approved version.

Back to the full Dazr Compliance overview › | Sign up free ›

ISO 27001 questions, answered.

How many controls does the platform cover?

All 93 Annex A controls in ISO 27001:2022, plus the Clause 4-10 management-system requirements (scope, leadership, planning, support, operation, performance evaluation, improvement). Each control has a description, recommendation and default review cadence.

Is this for stage-1 or stage-2?

Both. Stage-1 is documentation review; stage-2 is evidence sampling. Dazr keeps the SoA, the risk register, the incident register, control evidence and the activity log in one place for both.

Can I keep my Statement of Applicability in Dazr?

Yes. Mark each control applicable or not with a justification and implementation status, approve a version and export it as PDF or XLSX; excluded controls drop out of your control list. You can also keep linking an existing SoA document.

Will my external auditor accept evidence kept here?

Dazr gives auditors what they typically ask for: a timestamped activity log with the responsible person, evidence on each control, time-limited read-only auditor access and exports. Whether that evidence is sufficient is always the auditor's call.

Which ISO 27001 software is suitable for SMEs in the Netherlands?

Look for four things: the full ISO 27001:2022 control set with a Statement of Applicability, an interface in the language of the people who do the work, EU data storage, and a price that does not need a procurement project. Dazr Compliance covers all four: the control library (all 93 Annex A controls plus clauses 4-10) is in the free plan, the Statement of Applicability, the risk register, auditor access and up to five users come with Pro at €99 a month, the portal is in Dutch and in every other language of this website, and data stays in the EU.

Start your ISO 27001 program.