Home › Frameworks › SOC 2

SOC 2 audit readiness.

The Trust Services Criteria become 51 recurring controls with owners and evidence. Access reviews, change management and vendor reviews run on schedule, hosted in the EU. Included from Pro, €99 a month.

At a glance

  • Common Criteria (Security): CC1-CC9: control environment, communication, risk assessment, monitoring, control activities, logical and physical access, system operations, change management, risk mitigation.
  • Availability: A1: monitoring, capacity, environmental, BCP and recovery.
  • Processing Integrity: PI1: complete, accurate, timely, authorised processing.
  • Confidentiality: C1: identification and protection of confidential information.

On this page

  1. What is SOC 2?
  2. Who needs to comply
  3. Key SOC 2 controls covered by Dazr
  4. What auditors look for
  5. How Dazr helps with SOC 2

What is SOC 2?

SOC 2 (AICPA Trust Services Criteria). EU-based B2B SaaS selling into the US enterprise market, where SOC 2 reports are routinely demanded in procurement alongside ISO 27001.

Who needs to comply

  • EU-based B2B SaaS expanding into the US market
  • Data-platform and developer-tool companies serving US enterprises
  • AI / ML platforms whose customers ask for SOC 2 alongside ISO 27001
  • Healthcare-adjacent SaaS targeting US providers (often combined with HIPAA)

Key SOC 2 controls covered by Dazr

Common Criteria (Security)CC1-CC9: control environment, communication, risk assessment, monitoring, control activities, logical and physical access, system operations, change management, risk mitigation.
AvailabilityA1: monitoring, capacity, environmental, BCP and recovery.
Processing IntegrityPI1: complete, accurate, timely, authorised processing.
ConfidentialityC1: identification and protection of confidential information.
PrivacyP1-P8: notice, choice, collection, use, retention, disclosure, quality, monitoring, enforcement (aligned with GAPP).

What auditors look for

SOC 2 Type 2 auditors sample evidence over the audit period (typically 6 to 12 months): access reviews actually happened, changes were peer-reviewed, incidents were logged, vendors were reviewed. Dazr is the system of record across the period.

How Dazr helps with SOC 2

With Dazr Compliance you can:

  • Hold the Trust Services Criteria with linked controls and evidence
  • Run quarterly access reviews on cadence with email reminders
  • Track change management approvals and peer review evidence
  • Keep vendors in the vendor register with DPA and SOC 2 / ISO links and review dates
  • Hand the auditor a read-only view for sampling, or a single-PDF audit trail
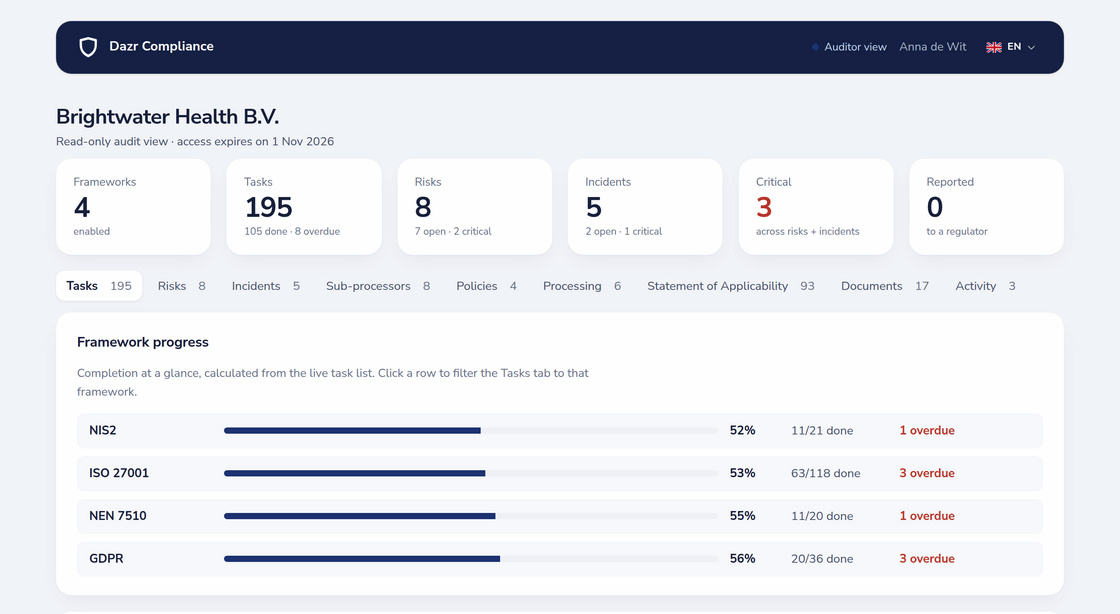
Read-only auditor view with time-limited access, framework progress and tabs for controls, risks, incidents, policies and the activity log
The auditor view: time-limited and read-only.

Back to the full Dazr Compliance overview › | Sign up free ›

SOC 2 questions, answered.

Does Dazr give us a SOC 2 report?

No. The SOC 2 report is issued by your CPA firm after their audit. Dazr is the system of record they will sample from. We do not perform the audit.

Type 1 or Type 2?

Type 1 attests design at a point in time; Type 2 attests operating effectiveness over a period. Dazr suits Type 2 well: recurring controls with dated evidence and the activity log show what was done across the audit window.

Does this work alongside ISO 27001?

Yes. Common Criteria and Annex A overlap heavily; the same evidence often serves both. Enable both frameworks in the same workspace.

Where is data hosted?

European Union only. Workspace records are encrypted at rest with AES-256-GCM at the application layer; uploaded evidence files rely on the storage provider's at-rest encryption. Italian entity, EU jurisdiction. SOC 2 is a US framework but the audit and infrastructure can be EU-based, and many US customers prefer that.

Start your SOC 2 program.