What is NIS2?
EU NIS2 Directive (Directive (EU) 2022/2555). Essential and important entities under NIS2: energy, transport, banking, financial market infrastructure, health, drinking water, waste water, digital infrastructure, ICT service management, public administration, postal and courier, food, chemicals, manufacturing, research.
Who needs to comply
Whether you are essential or important depends on the sector in Annex I or II of the Directive and on your size. The NIS2 scope checker applies the same rules.
- Annex I sectors (energy, transport, banking, financial market infrastructure, health, drinking water, waste water, digital infrastructure, ICT service management, public administration and space): essential if large, important if medium-sized.
- ICT service management covers managed service providers (MSPs) and managed security service providers (MSSPs) serving business customers. An MSP with 150 staff is usually medium-sized, so an important entity; above the medium-sized ceilings it is essential.
- Annex II sectors (postal and courier, waste management, chemicals, food, manufacturing, digital providers and research): important if medium-sized or large.
- Regardless of size: qualified trust service providers, TLD name registries, DNS service providers and central government are essential; public electronic communications providers and non-qualified trust service providers are essential if they are large or, for electronic communications, medium-sized, and important otherwise.
- Below the threshold: micro and small enterprises in Annex I and II sectors are out of scope unless the size-independent rules above apply or the authority designates them.
Medium-sized means 50 to 249 staff, and an annual turnover up to €50 million or a balance sheet total up to €43 million (Commission Recommendation 2003/361/EC); large is above those ceilings. National laws can add sectors or identify smaller entities; Italy, for example, adds its own annexes.
Key NIS2 controls covered by Dazr
National transposition
As of 19 October 2026. NIS2 is a directive, so the duties you actually face come from your national law and authority.
Ready-made national frameworks. Next to EU NIS2, Dazr includes Italy’s ACN baseline measures (ACN) and Czechia’s NÚKIB measures under Decrees 409/2025 and 410/2025 (NÚKIB) as frameworks of their own, with the national reporting deadlines.
More country guides, in the local language. Österreich: NISG 2026 · Česko: zákon č. 264/2025 Sb. · Slovensko: zákon č. 69/2018 Z. z. · România: OUG nr. 155/2024 · Sverige: cybersäkerhetslagen · Danmark: NIS2-loven · Norge: digitalsikkerhetsloven · Portugal: Decreto-Lei n.º 125/2025 · España: estado de la ley · France: loi Résilience.
Implementing Regulation (EU) 2024/2690. For DNS service providers, TLD registries, cloud and data-centre providers, content delivery networks, managed (security) service providers, online marketplaces, search engines, social networks and trust service providers, this Commission regulation spells out the technical and methodological requirements behind the Article 21 measures and when an incident counts as significant. See the 2024/2690 checklist and the significant-incident checker.
Sources: Directive (EU) 2022/2555, Implementing Regulation (EU) 2024/2690, Forvis Mazars on the Cbw, D.Lgs. 138/2024, CCB, NIS2UmsuCG, NIS2 w Polsce (biznes.gov.pl).
What auditors look for
NIS2 specifically requires evidence of management body approval, supply-chain risk assessments, and the 24-hour early warning / 72-hour intermediate / 1-month final report incident notification cycle. Dazr holds the evidence for all three.
How Dazr helps with NIS2
With Dazr Compliance you can:
- Maintain the Article 21 cybersecurity risk-management measures as recurring controls
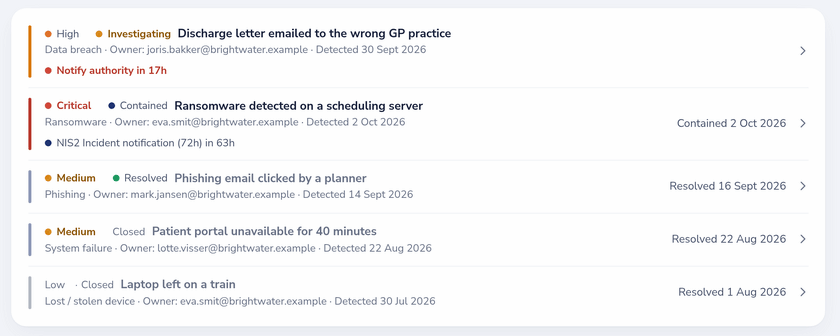
- Run the incident register with the 24h / 72h / 1-month notification timestamps and authority case references
- Review suppliers in the vendor register with DPA and certificate links, review and expiry dates (Pro and Enterprise)
- Hold the management body approval date on the compliance profile, refreshed annually
- Hand the competent authority a single-PDF audit trail or a read-only view
Back to the full Dazr Compliance overview › | Sign up free ›