Where your data lives
All application data and backups are stored in the EU, under EU jurisdiction. Dazr is an Italian company (VAT IT 02801250065). The portal has no analytics pixels or third-party trackers.
Encryption
Workspace records (controls, risks, incidents, intake reports, the activity log, member and profile data and the other registers) are encrypted at rest with AES-256-GCM at the application layer, on top of the hosting provider's own at-rest encryption. Uploaded files such as evidence and attachments rely on the storage provider's at-rest encryption, sit under unguessable URLs and are only served through an authenticated download; they are not additionally encrypted by the application. Transport is HTTPS only.
Sign-in and sessions
- Sign in with Google, Microsoft or a one-time code sent to your work email, on every plan. Dazr stores no passwords.
- Every request is checked against current membership and scoped to your workspace, so a removed member loses access at once.
- "Sign out everywhere" revokes all sessions of an account.
- Sign-in, public reporting and API endpoints are rate-limited.
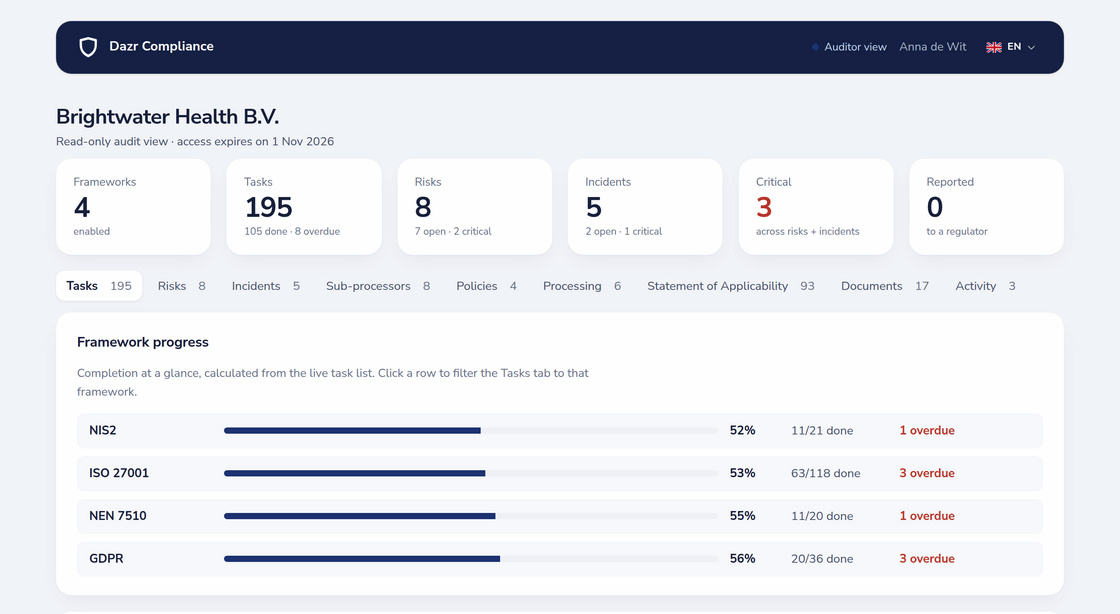
- External auditors verify with a one-time code per visit and get access for 1 to 60 days, revocable at any time.
Roles and access
| Role | Can |
|---|---|
| Owner | Everything, including billing, ownership transfer and deleting the workspace |
| Admin | Manage frameworks, registers, members, auditors and settings |
| Member | Work on assigned controls and incidents, read the registers, acknowledge policies |
| Auditor | Read-only access for a set period, comments on controls and notes on incidents |
An activity log you can search
Who did what and when, for every state-changing action, including actions taken by Dazr support; when support steps into a workspace, the workspace gets an email. Search it, filter it by type and date, and export it. It keeps the most recent 2,000 events on Free, 5,000 on Basic, 25,000 on Pro and 50,000 on Enterprise.
Contracts and data rights
- A Data Processing Agreement covers Dazr as your processor under the GDPR.
- The sub-processor list is published, with 30 days' notice before a sub-processor is added or changed.
- Export every register as Excel and CSV at any time; the owner can delete the workspace.
- Report a vulnerability to security@dazr.eu.