What is EU AI Act?
EU AI Act (Regulation (EU) 2024/1689). Providers and deployers of AI systems placed on the EU market: developers of general-purpose AI, providers of high-risk AI in safety, hiring, education, credit scoring, biometric ID, law enforcement, migration, justice, and any deployer using a high-risk AI in those sectors.
When the AI Act applies
As of 1 October 2026. The Digital Omnibus on AI, Regulation (EU) 2026/1744, was published in the Official Journal on 24 July 2026 and entered into force on 27 July 2026. It moved the high-risk deadlines; the earlier milestones stay as they were.
- 2 February 2025: prohibited practices (Article 5).
- 2 August 2025: obligations for general-purpose AI models.
- 2 August 2026: most transparency obligations (Article 50), governance and penalties.
- 2 December 2027: high-risk AI systems listed in Annex III (employment, education, credit, essential services, biometrics, critical infrastructure, law enforcement, migration, justice). Previously 2 August 2026.
- 2 August 2028: high-risk AI that is a product or safety component under the Annex I harmonisation legislation. Previously 2 August 2027.
Sources: Regulation (EU) 2024/1689 on EUR-Lex and Regulation (EU) 2026/1744 on EUR-Lex. Read the AI Act timeline after the Digital Omnibus for what moved and why.
Who needs to comply
- Providers of high-risk AI systems listed in Annex III (employment, education, credit, biometric ID, critical infrastructure, justice, migration)
- Providers of general-purpose AI models, including those with systemic risk
- Providers of AI systems with transparency duties under Article 50, such as chatbots and generators of text, images, audio or video, including AI features inside ordinary apps and devices
- Every organisation that uses AI at work, for AI literacy (Article 4)
- Deployers of high-risk AI systems in their own operations
- Importers and distributors of AI systems on the EU market
- Public authorities deploying AI in regulated contexts
Your role, your risk, your plan
The AI Act sorts obligations by your role (provider or deployer) and by the risk of the system. Find your row:
| Your role and the risk | What applies | Dazr plan |
|---|---|---|
| Deployer of minimal- or limited-risk AI: you use AI tools from others, such as an AI assistant or the AI in your CRM | AI literacy for staff (Article 4), no prohibited practices (Article 5), and disclosure when you publish deepfakes or AI-written text on matters of public interest (Article 50) | Every plan, including Free |
| Provider of a limited-risk feature (Article 50): a chatbot, assistant or generator of text, images, audio or video in your own app or device | Article 4 and 5, plus Article 50: tell people they are dealing with AI and mark generated content in a machine-readable way. No conformity assessment and no CE marking under the AI Act | Every plan, including Free |
| Deployer of high-risk AI (Annex III), such as CV screening or credit scoring | Article 26: use it as instructed, human oversight, keep the logs, inform workers and the people affected; a fundamental-rights impact assessment (Article 27) for public bodies and some private deployers | Article 26 on every plan; the impact assessment on Enterprise |
| Provider of high-risk AI (Annex III, or a safety component of a product under Annex I) | Articles 9-20: risk management, data governance, technical documentation, logs, human oversight, quality management, conformity assessment, CE marking, registration in the EU database, post-market monitoring and serious-incident reporting | Enterprise |
| Provider of a general-purpose AI model (GPAI) | Article 53: technical documentation, information for downstream providers, a copyright policy and a summary of the training content; Article 55 on top for models with systemic risk | Enterprise |
Where an AI feature in an ordinary product fits. Most software and device makers that add AI, for example a support chatbot or a writing assistant on top of a hosted language model, are the provider of a limited-risk AI system. Article 50 applies to them, the high-risk rules do not, unless the feature is used for an Annex III purpose or is a safety component of a regulated product. Building on someone else's model does not make you a GPAI model provider. That fits on every plan, including Free.
Key EU AI Act controls covered by Dazr
What auditors look for
Market-surveillance authorities check three things: that you classified your system correctly (prohibited / high-risk / limited / minimal), that the technical documentation in Annex IV exists and is current, and that the post-market monitoring and serious-incident reporting (Article 73) actually runs. Dazr holds the evidence.
How Dazr helps with EU AI Act
With Dazr Compliance you can:
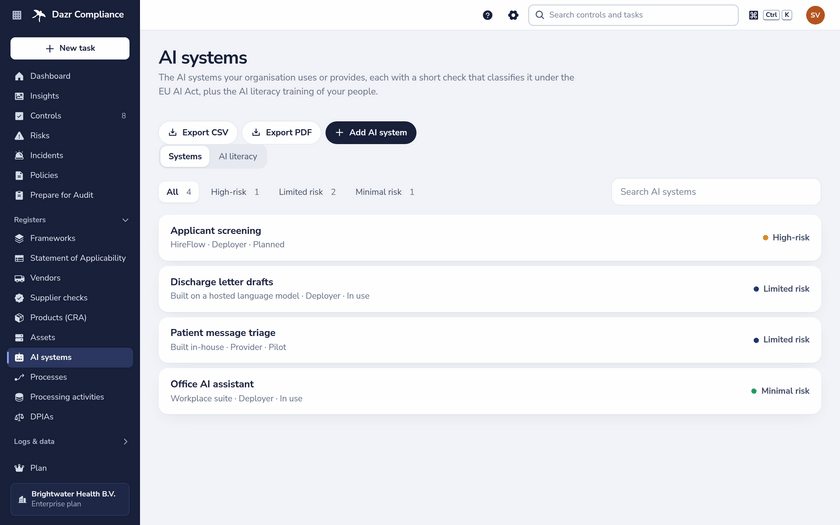
- Keep an inventory of the AI systems you provide or deploy, with role, users and data, and classify each one with a short guided check that shows the reasons and the controls that apply
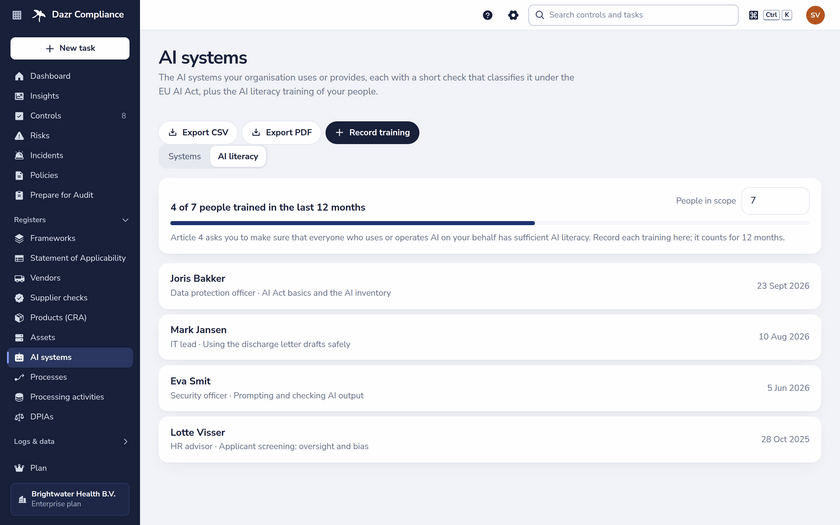
- Record who received AI literacy training, when and on what, with the certificate, and see coverage over the last 12 months (Article 4)
- Export the AI inventory and the training records as CSV or PDF
- Hold the Annex IV technical documentation links and refresh on cadence
- Run the risk-management system as recurring controls per Article 9
- Track post-market monitoring metrics and reviews per Article 72
- Log serious incidents in the incident register with timestamps and authority case references, against the Article 73 deadlines
- Hand the market-surveillance authority a single-PDF audit trail or read-only view
Back to the full Dazr Compliance overview › | Sign up free ›