Home › Frameworks › GDPR

GDPR compliance, with the evidence.

Recurring GDPR controls and a breach register with a 72-hour countdown, free. From Pro, your records of processing and DPIAs sit next to the vendors and risks behind them. Hosted in the EU.

When did you become aware?

Indicative. Clocks run from awareness; check your national law and the full calculator for options such as trust service providers or a fix date.

Article 6, 9Lawful basis records and special-category checks per processing activity.
Article 28Vendor and sub-processor register with DPA URLs and review dates (Pro and Enterprise).
Article 30Records of processing activities as a register, linked to the vendors involved.
Article 32Technical and organisational measures, with controls shared with ISO 27001 if both are enabled.

What is GDPR?

EU General Data Protection Regulation. Any organisation processing personal data of EU residents: SaaS vendors, e-commerce, healthcare, finance, public sector, education.

Who needs to comply

  • B2B SaaS companies serving EU customers
  • Health-tech, fintech and edtech with sensitive personal data
  • E-commerce and marketing operators handling EU consumer data
  • Public-sector and non-profit organisations under GDPR scope

Key GDPR controls covered by Dazr

Article 6, 9Lawful basis records and special-category checks per processing activity.
Article 28Vendor and sub-processor register with DPA URLs and review dates (Pro and Enterprise).
Article 30Records of processing activities as a register, linked to the vendors involved.
Article 32Technical and organisational measures, with controls shared with ISO 27001 if both are enabled.
Article 33-34Breach register with regulator-notification fields and 72-hour clock.
Article 35DPIA register linked to processing activities and risks, plus a recurring review.

What auditors look for

Supervisory authorities sample evidence: ROPA is up to date, breach register exists and is populated, sub-processor changes follow notice, DPIAs exist for high-risk processing. The platform holds each one.

How Dazr helps with GDPR

With Dazr Compliance you can:

  • Keep records of processing in the Article 30 register, or link your existing ROPA and review it on cadence
  • Run the breach register with severity, timestamps, regulator-notification block and root cause
  • Maintain the sub-processor register with DPA URLs, review dates and contract-expiry flags (Pro and Enterprise)
  • Track DPIAs as recurring controls per high-risk processing activity
  • Hand the supervisory authority a clear audit trail when sampled
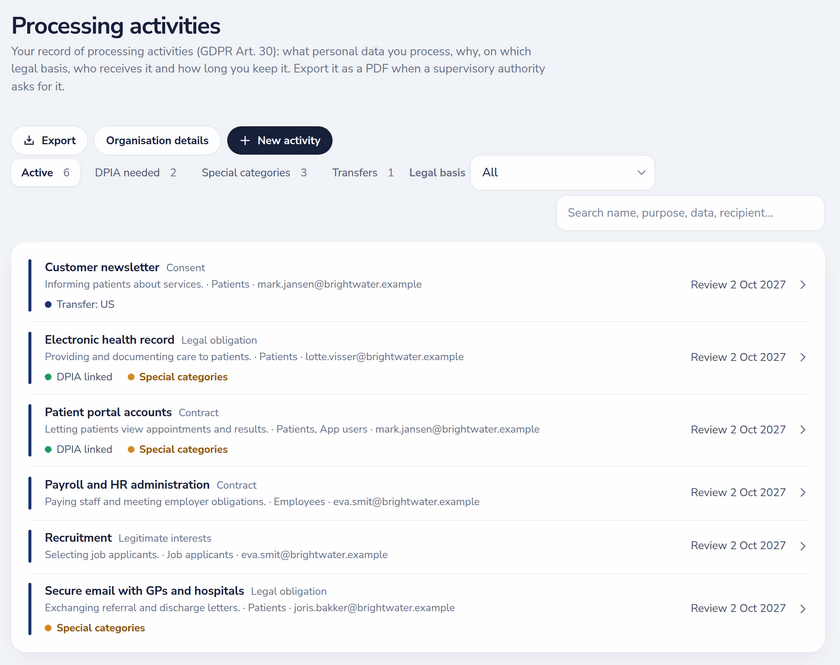
GDPR Article 30 record of processing activities with legal basis, data subjects, special categories, transfers and linked DPIAs
Processing activities with legal basis, transfers and DPIAs.

Back to the full Dazr Compliance overview › | Sign up free ›

GDPR questions, answered.

Does Dazr file the breach notification with the supervisory authority for me?

No. Dazr holds the Article 33 notification fields, timestamps every state change and shows a 72-hour countdown on the incident, but the filing itself goes through your authority's portal. Work out a deadline with the free breach deadline calculator.

Can I use Dazr alongside an external DPO?

Yes. Record the DPO's name and email in the compliance profile, and add them as a member (or as a read-only auditor) so they see the registers and receive reminders.

Where is data hosted?

European Union only. Workspace records are encrypted at rest with AES-256-GCM at the application layer; uploaded evidence files rely on the storage provider's at-rest encryption.

Is Dazr a sub-processor?

Yes. We are an Italian GDPR Article 28 sub-processor of yours; the DPA at /legal/dpa activates automatically when a workspace is created and we publish the current sub-processor list at /legal/subprocessors.

Start your GDPR program.